The Department of Homeland Security's year-old drone acquisition office has put out a new market survey that reads like a checklist of everything the department has learned not to trust: cloud servers it doesn't control, unencrypted radio links, and components with murky foreign origins. The Program Executive Office for Unmanned Aircraft Systems and Counter-Unmanned Aircraft Systems (PEO for UAS/C-UAS) issued the request for information under the DHS Drone Development Program, and it wants industry's answers by Oct. 5, 2026, according to a report published Sept. 23 by GovCon Wire.
The RFI is narrow but pointed. DHS is looking for small unmanned aircraft systems that are lightweight and rapidly deployable, that do not depend on cloud connectivity to operate, and that support AES-256 encrypted command-and-control, data, and video links. Vendors also need to show compliance with the Defense Innovation Unit's Blue UAS and Green UAS standards, and they need to minimize foreign components, software, firmware, and manufacturing in the aircraft they propose.
Individually, none of those requirements is new to federal drone buying. Together, they describe a very specific kind of aircraft: one that can be flown by a Border Patrol agent or FEMA responder somewhere without reliable connectivity, without leaking video or telemetry to a server outside DHS's control, and without carrying components that could be traced back to a foreign supply chain the department doesn't trust.
Who's Running the Office, and Why It Exists
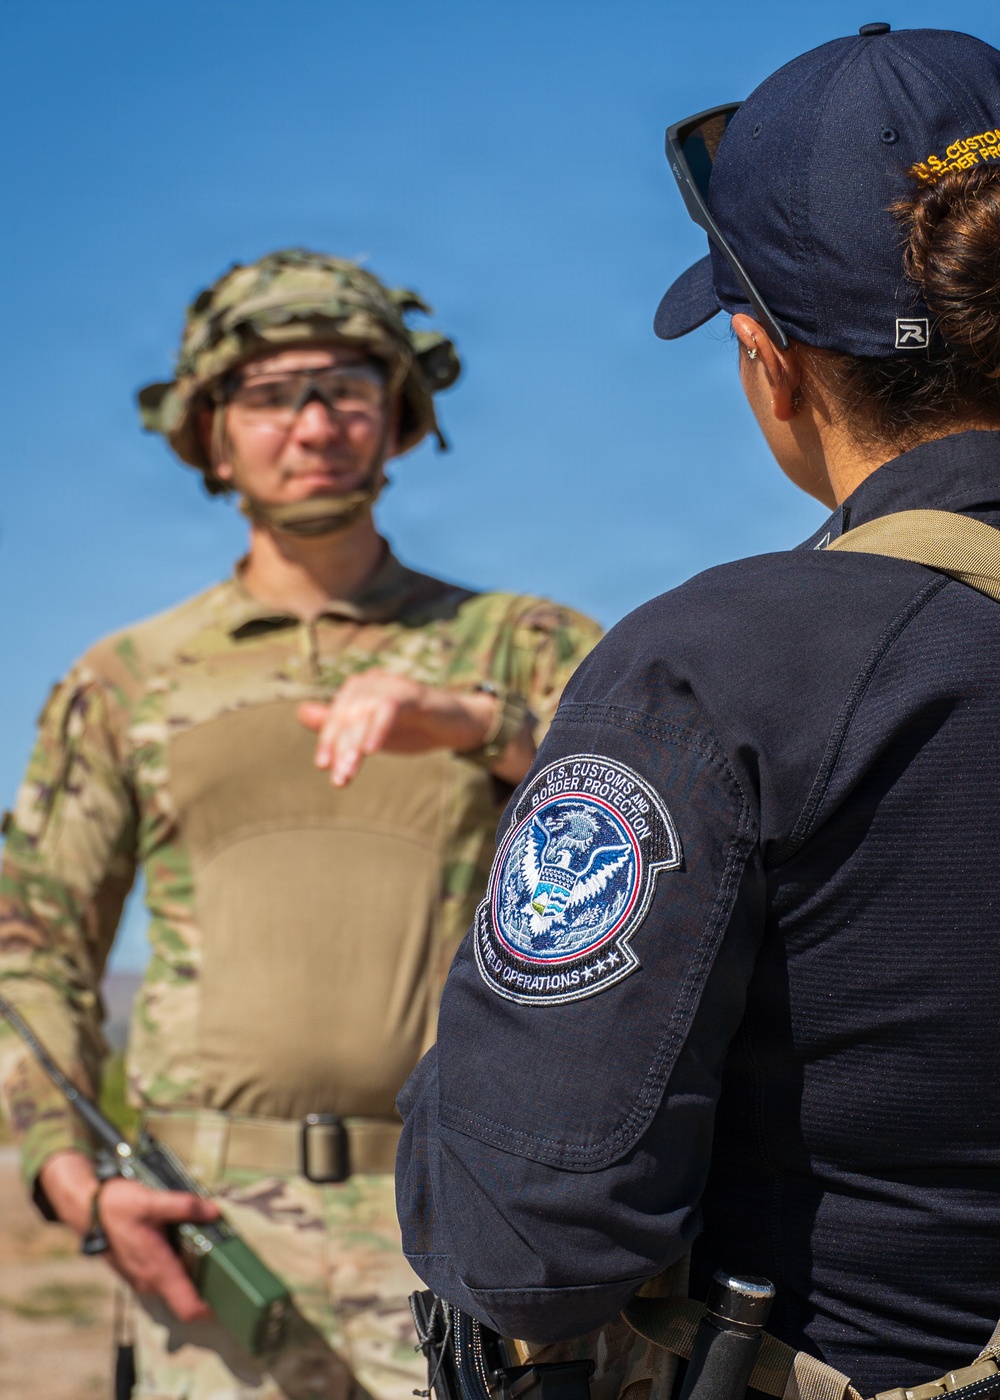
The PEO for UAS/C-UAS is young. DHS announced it in a Jan. 12, 2026 press release, describing an office built to oversee the department's strategic investments in both drones and counter-drone technology. The launch announcement leaned hard into the year's marquee security events: the office was finalizing a $115 million investment in counter-drone technology to help secure venues for the America250 celebrations and the 2026 FIFA World Cup, both drawing major security demands to U.S. venues this year. Then-Secretary Kristi Noem framed the stakes bluntly in that release, saying "drones represent the new frontier of American air superiority." Eight months later, the office has a face and a mandate GovCon Wire's Elodie Collins lays out in detail: executive director Steven Willoughby, who described the PEO's job as being the department's "belly button" — the single point that keeps drone and counter-drone acquisition consistent across DHS's sprawling list of components, from Customs and Border Protection to the Transportation Security Administration to the Coast Guard. Before the PEO existed, each component bought and fielded its own drones and counter-drone gear more or less independently, which is exactly the kind of fragmentation a "belly button" office is designed to fix.
What DHS Is Actually Asking For
The RFI itself is a response to a problem that has dogged federal small-UAS buying for years: most commercial drones, and a fair number of drones built for the U.S. government market, still lean on cloud infrastructure for flight logging, firmware updates, or live video relay. That's a liability for an agency whose field units may operate in denied, degraded, or simply remote connectivity environments — a stretch of border fence, a disaster zone with no cell service, a port facility during an incident. A drone that needs to phone home to fly, or that streams video through a third-party cloud service, is both an operational risk and a potential data-exposure risk. The AES-256 encryption requirement addresses a related but distinct concern: interception. Command-and-control links, telemetry, and video downlink are all attack surfaces if they're unencrypted or weakly encrypted, whether the threat is a criminal actor with an SDR or a foreign intelligence service. Requiring AES-256 sets a floor rather than breaking new ground, but it signals DHS wants that floor enforced consistently across every component that buys through the PEO. Blue UAS and Green UAS are DIU's vetted-hardware and vetted-software lists, respectively, built to give federal buyers a pre-vetted supply chain to draw from without each agency running its own review from scratch. Requiring compliance with both, plus a broader instruction to minimize foreign components, software, firmware, and manufacturing, tracks with a now-familiar federal posture: DHS doesn't just want drones that pass a specific banned-manufacturer list, it wants a supply chain it can vouch for end to end.
The Counter-Drone Half of the Mandate
The PEO's name has two halves, and the counter-UAS side has been busier publicly so far. GovCon Wire reports the office will spotlight counter-drone work at the 2026 Homeland Security Summit on Nov. 10, with panels drawing speakers from CBP's C-UAS Defense Capability Group and its Border Enforcement and Management Systems Directorate. That counter-UAS push isn't happening in isolation. DHS's Science and Technology Directorate has been working the acquisition side of the same problem from a different angle. In May, the department's National Urban Security Technology Laboratory (NUSTL) released a free C-UAS Purchasing Tool, aimed at first responders rather than large federal components, according to a report from ExecutiveGov. The tool gives agencies standardized scorecards to compare vendor counter-drone systems against factors like terrain, budget, and local RF environment — useful for a fire department or police agency trying to spend FEMA counter-UAS grant money wisely without an in-house team of RF engineers. NUSTL Director Alice Hong was quoted describing the tool's purpose in that release. It's a smaller, more localized effort than the PEO's RFI, but it points at the same underlying gap: counter-drone technology varies wildly by environment, and DHS has been building tools — both acquisition offices and literal scorecards — to help buyers at every level make sense of it.
Why It Matters
For drone manufacturers and integrators, the RFI is a preview of what a DHS-wide small-UAS contract vehicle is likely to require going forward, not just a one-off solicitation. A "belly button" office exists specifically to standardize requirements across components, so a vendor that meets this RFI's bar on cloud independence, AES-256 encryption, Blue/Green UAS compliance, and supply-chain minimization is positioning itself for more than a single CBP or FEMA buy — it's positioning for whatever follows once the PEO consolidates demand. It also matters because it reflects where federal small-UAS policy has been heading since the Blue UAS program itself launched: away from convenience-first commercial platforms and toward aircraft built from the ground up to survive government scrutiny on supply chain, security, and connectivity. An RFI with an Oct. 5 response deadline is early in the process — it's a market survey, not a solicitation — but it tells industry precisely which boxes the eventual buy will require checking, well before money moves. And with the PEO putting counter-UAS in front of the same Homeland Security Summit audience seven weeks later, the office is signaling both halves of its mandate — arming DHS with drones it trusts, and defending against the ones it doesn't — are moving on parallel, not sequential, tracks.